Project 01
Mini-SOAR
Alert enrichment and threat hunting in Python
- Enriches new alerts as they come in - risk level, recommended steps, the reasoning behind security findings, mapping to MITRE ATT&CK
- Hourly threat hunting across all Windows/AD logs: detects password spraying, Kerberoasting, DCSync and other attack techniques
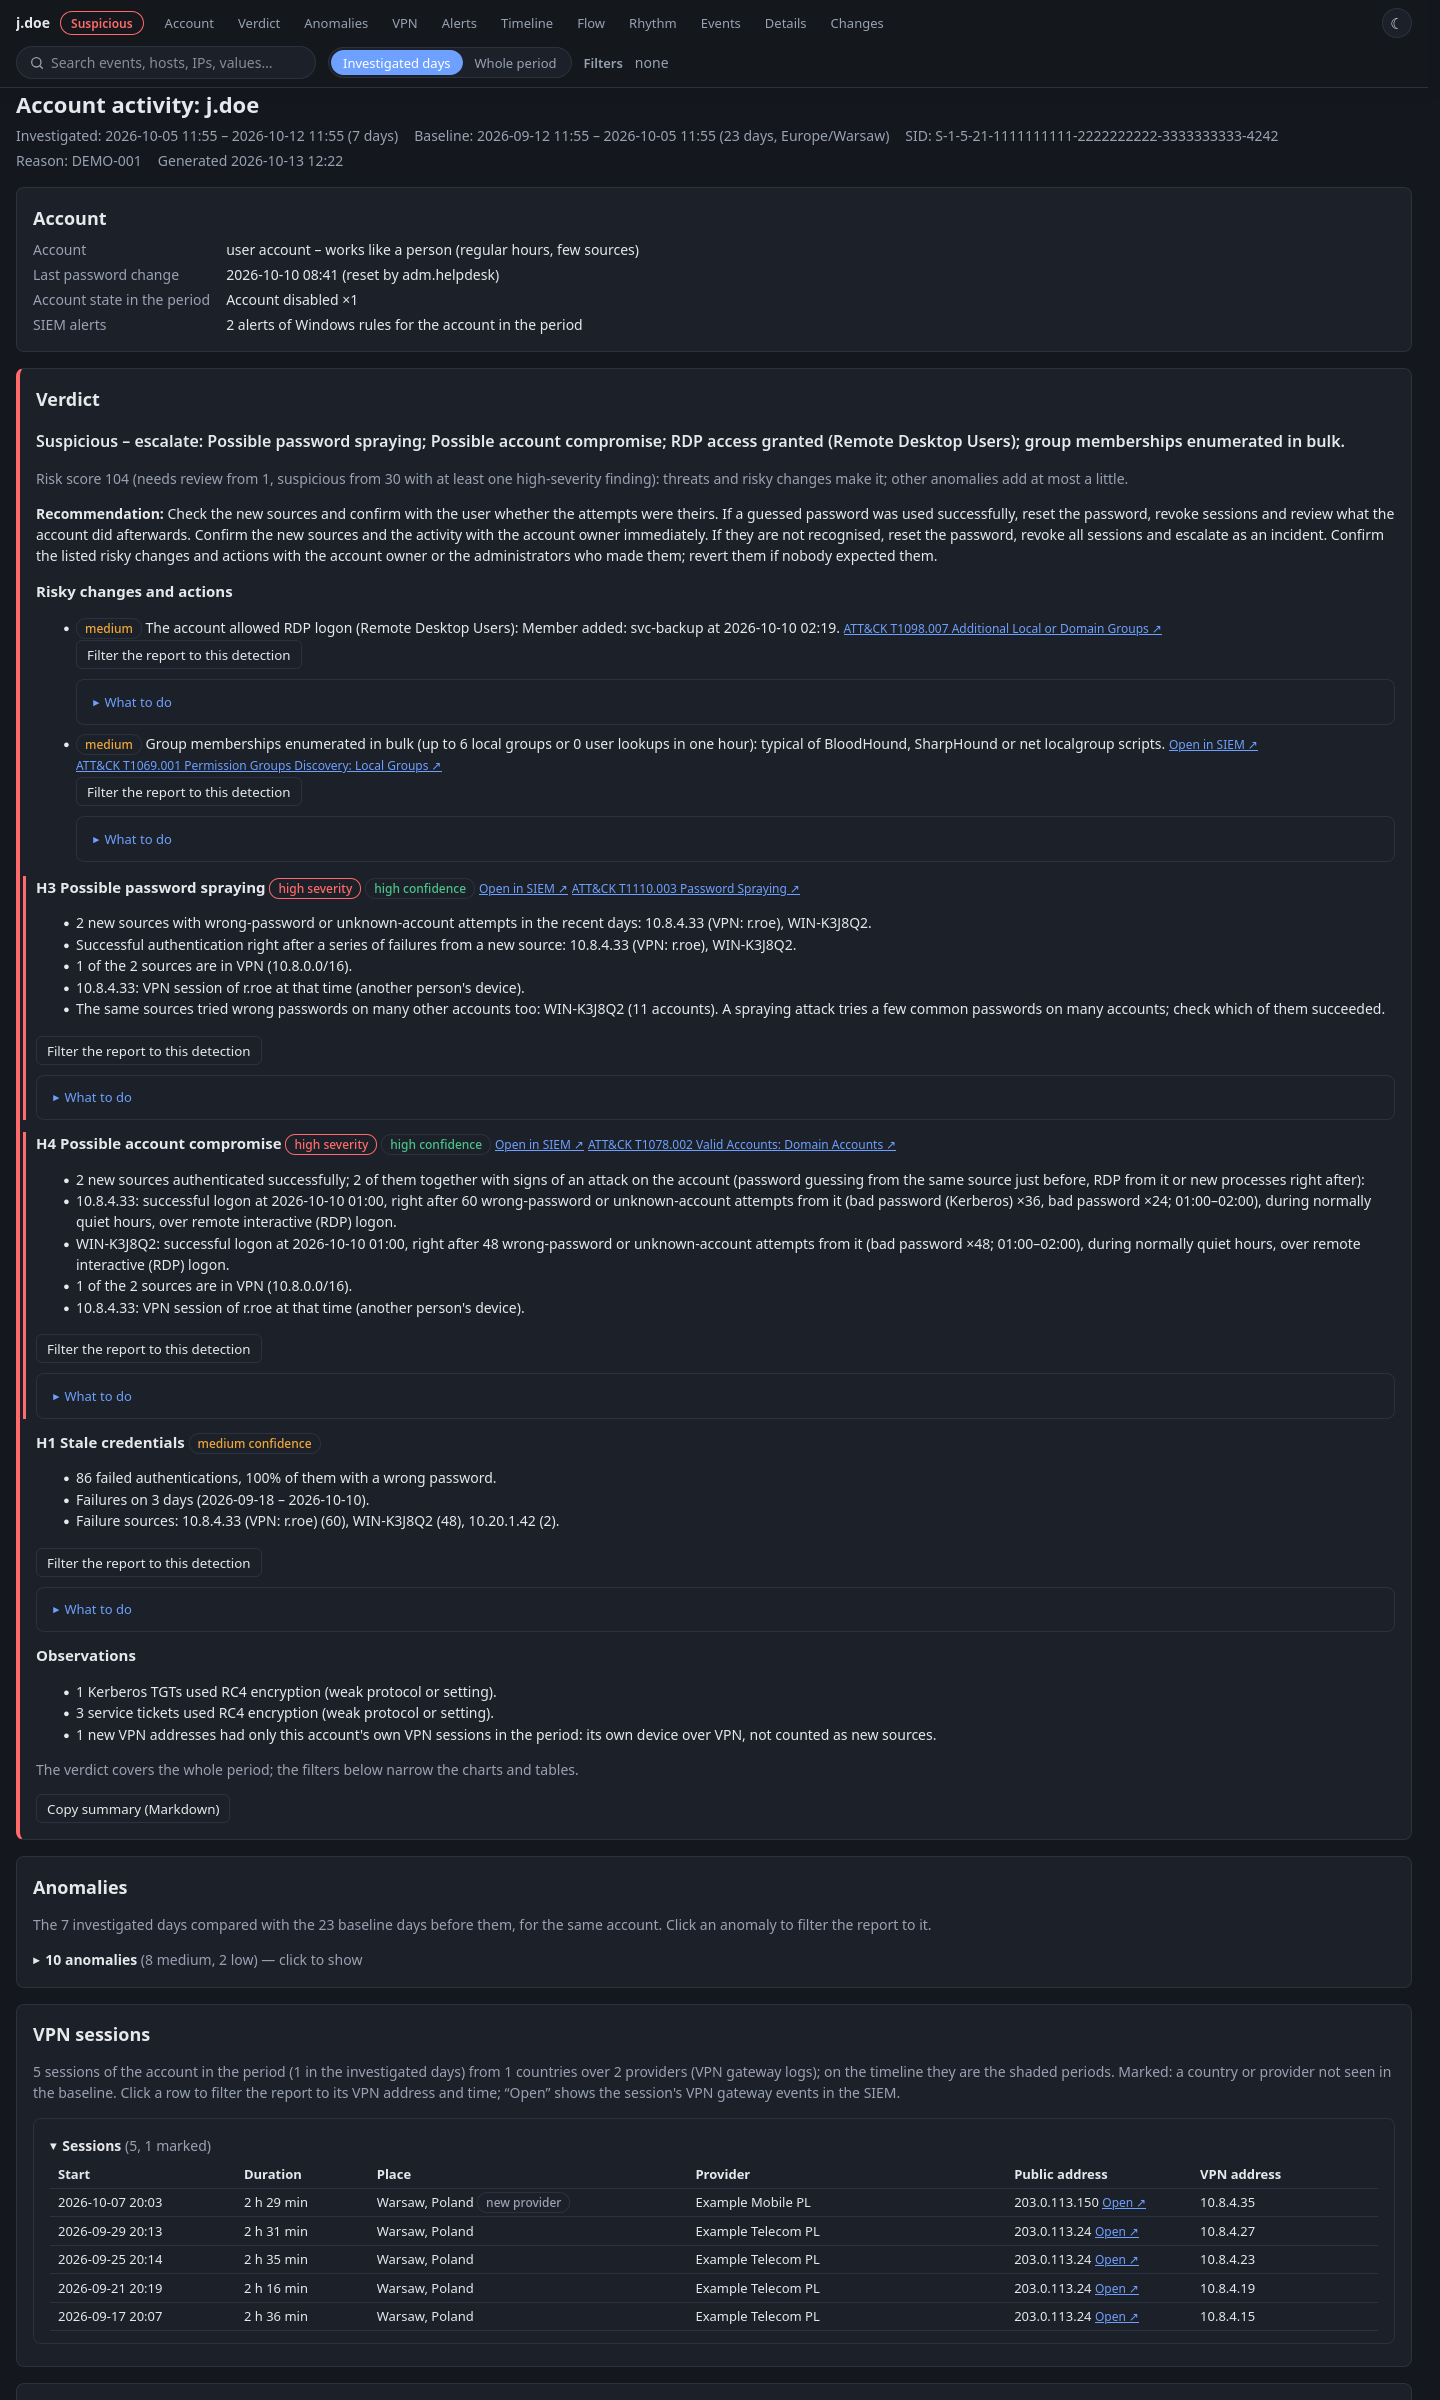
- VPN session attribution and the user account analyzer with an HTML report
Input
- new Windows alerts in the SIEM (OpenSearch)
- Windows and Active Directory events
- VPN gateway logs
Engine (Python)
- every 90 s - enrichment
- hourly - threat hunting
- 01alert parser
- 02targeted context queries
- 03per-event-type analysis module
- 04SigmaHQ rules (pySigma)
- 05verdict: risk, rationale, MITRE ATT&CK
SQLite · systemd - state, retries, backlog
Output
- enriched alert
- hunting findings, without hourly duplicates
- HTML report for an account or event type (PowerShell script)